BSIDES BELGRADE 2026
AGENDA 2026
 GO BACK TO AGENDA
Bring Your Own Chaos: A Practical Guide to BYOVD and EDR Evasion
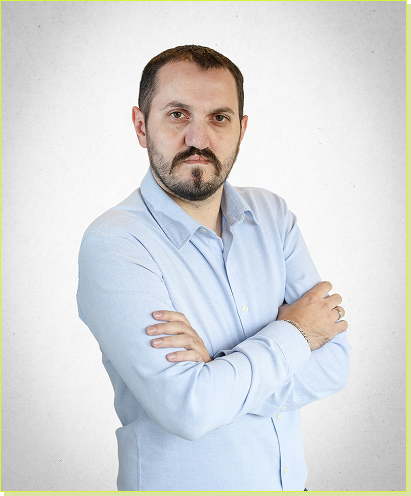
SPEAKERS: Miloš Skalušević


About the Workshop/Talk
Endpoint Detection and Response (EDR) agents are designed to be the ultimate authority on a Windows system. They reside in both User and Kernel mode, utilizing Protected Process Light (PPL) and "Watchdog" services to ensure that even a Local Administrator cannot simply "End Task" their way to freedom. But these agents have a blind spot: the Windows trust model itself. In this talk, we will demonstrate the BYOVD (Bring Your Own Vulnerable Driver) technique to dismantle modern security stacks. We will explore how a legitimately signed driver, despite its flaws, can be used as a bridge to Ring 0.
Key takeaways:
- Beyond Access Denied: A technical breakdown of why standard process termination tools fail against PPL-protected security agents.
- The BYOVD Bridge: How to weaponize signed drivers to gain arbitrary kernel-mode execution.
- Winning the Race: A deep dive into the Watchdog Race Condition. We will show how a persistent, low-level termination loop in Rust can outpace the Service Control Manager's recovery logic.
- The Power of Persistence: Why keeping a kernel handle open and constantly polling for target PIDs is more effective than a one-time kill.
We will conclude with a live demo showing a real-time battle between a custom Rust orchestrator and an EDR's self-healing mechanisms, effectively rendering the security stack useless in a matter of seconds.